Retainer capacity is full until mid-2027.Fixed-scope projects available on request.
Custom security training
We do this work, and we teach it.
Every session is built from real engagements, for the people in the room.
- CZ / EN
- on-site or remote
- custom-built
- quoted on request
This training can be booked on its own, or scheduled for you inside the Retained Security Partner retainer at the point where it adds the most.
Track Record
Past engagements
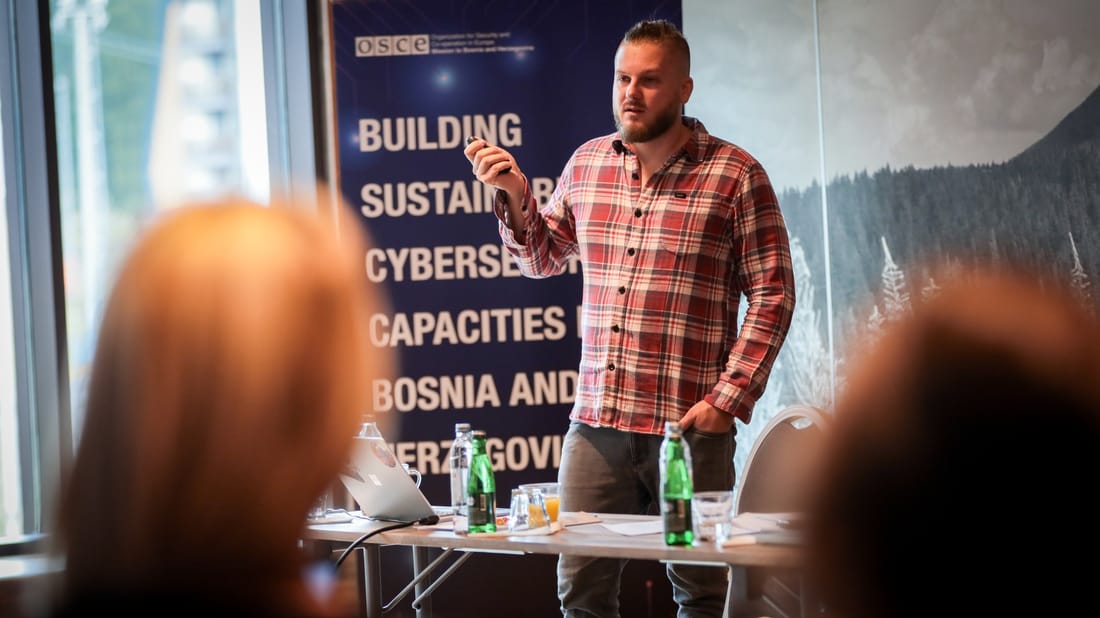
Building Sustainable Cybersecurity Capacities in Bosnia and Herzegovina
A dual-session workshop series for women professionals, covering AI security, risk management, and incident response.
Partners: OSCE, Women4Cyber, Embassy of the Czech Republic in Sarajevo
Train-the-Trainers Program on Cybersecurity for MSMEs
A capacity-building programme delivering 15 days of specialised train-the-trainer curriculum and 20 days of direct consulting to strengthen cybersecurity in Bosnian MSMEs.
Partners: UNDP, CzechAid
Instructor Work
Teaching beyond client work
Instructor sessions for two organisations that bring new people into IT and security.
Czechitas
Workshops and mentoring for people moving into IT and security from another career, on the Czech non-profit's retraining programmes.
Women4Cyber
Repeat speaker and trainer at Women4Cyber events, including the OSCE workshop series for women professionals in Bosnia and Herzegovina.
The Problem
The human risk
68%
of breaches involved a non-malicious human element
Verizon DBIR 2025
Most of them come down to a rushed click, a reused password or an invoice that looked right. Training moves that number only when people practise more than once a year.
The Solution
Training for every level
For IT Professionals
For End Users
How We Train
Delivery formats
Hands-On Technical Labs
Attack & defend in live environments
Tabletop Exercises
Simulated incident pressure - now a dedicated service →
Interactive Workshops
Built around discussion and your own cases
CTF Challenges
Built to order for your stack, so the build time is scoped and quoted with the training
What We Can Cover
Training topics
Four areas drawn from our client work. Each training starts with a conversation about what your team needs, and any relevant subject can become a session.
Offensive security
How an intrusion progresses: Active Directory attack paths, web and API testing, and the social engineering that opens the door. Delivered as a hands-on lab.
Defensive operations
Microsoft Sentinel and Defender, log analysis, detection and response, identity in Entra ID, and running vulnerability management so the findings arrive as a work queue someone owns.
Governance, risk and compliance
Cyber risk management, ISO 27001 implementation, NIS2 and GDPR, supplier risk, and writing policies people follow.
Executive and board
Cyber risk in the language a board decides in, the AI and regulatory picture, and tabletop exercises that put the leadership team under a realistic incident.
Get started
Scope a programme
Training is quoted on request. Every programme is built for one audience, so the figure follows the audience size, the number of days, the delivery format, and how much material and lab or CTF infrastructure has to be built. Daily and project rates both work.